Joomla Admin Login Backdoor Shell
Backdoor ShellThe 'Joomla Admin Login Backdoor Shell' is a specialized tool designed for penetration testing and security auditing, enabling authorized users to bypass Joomla admin authentication mechanisms. This tool facilitates controlled testing of Joomla-based websites' security robustness.
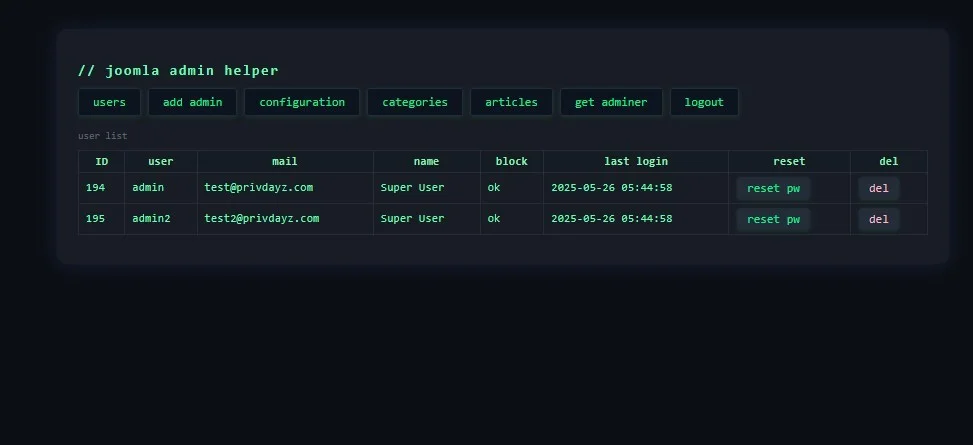
Features
About Joomla Admin Login Backdoor Shell
The Joomla Admin Login Backdoor Shell is a specialized PHP web shell tool designed primarily for backend server management and security auditing within Joomla-based environments. This powerful tool facilitates penetration testing by allowing ethical hackers to mimic advanced bypass techniques typically used in unauthorized access scenarios. By employing this shell, security professionals can conduct thorough vulnerability assessments, ensuring that any potential security flaws within the Joomla administrative framework are identified and mitigated. The shell's capability for remote execution plays a critical role in simulating real-world attacks, where attackers might exploit vulnerabilities to gain unauthorized access to backend systems. Ethical hackers utilize this tool to enhance the security posture of Joomla installations by testing and validating the effectiveness of existing security measures. Additionally, the Joomla Admin Login Backdoor Shell serves as an educational resource for IT security students and professionals aiming to deepen their knowledge in areas such as ethical hacking and penetration testing. Its use in controlled, authorized environments helps organizations strengthen their defenses against potential cyber threats, making it an indispensable part of proactive cybersecurity strategies.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.