pHpmyadmin Shell
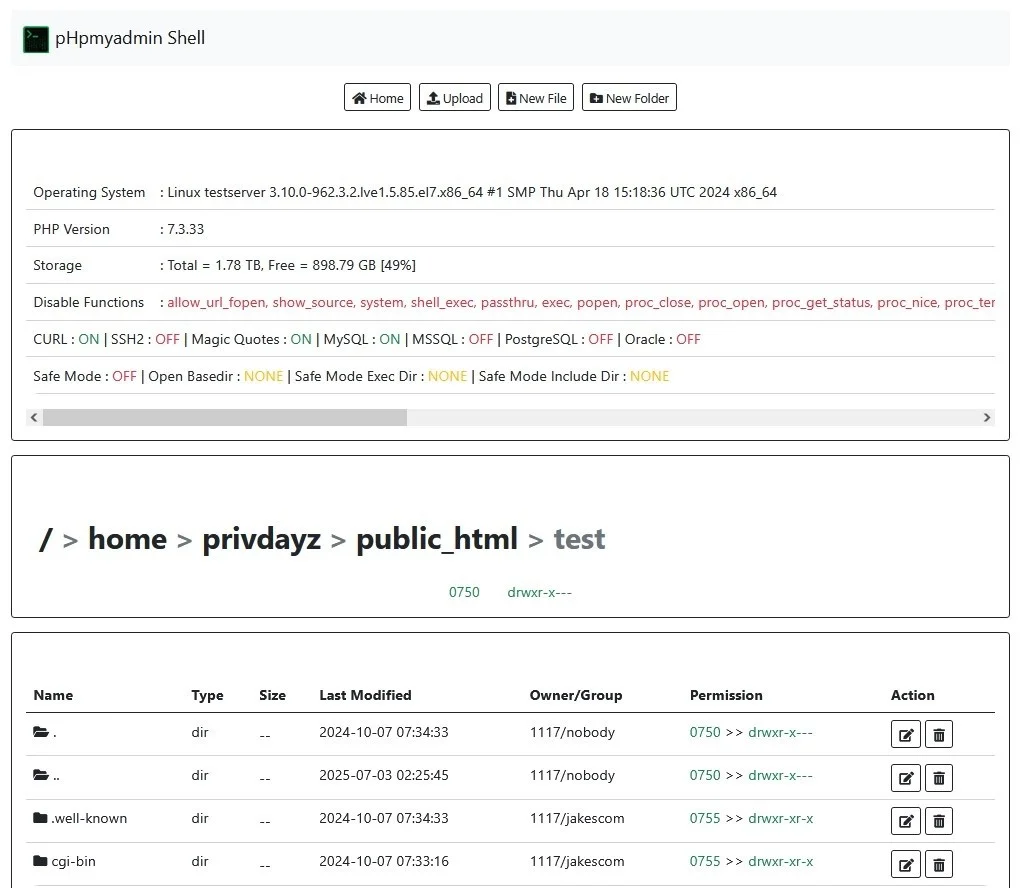
Bypass Shell'Phpmyadmin Shell' enables advanced penetration testing and security auditing by facilitating server control and environment manipulation to bypass standard access controls. This tool is designed for authorized security professionals to enhance system defenses.
Features
About pHpmyadmin Shell
The 'pHpmyadmin Shell' is a specialized tool used primarily in security auditing, designed to manage backend servers through a web-based interface that mimics popular database management systems. This tool facilitates penetration testing by allowing ethical hackers to simulate and execute commands on a server as if they have administrative rights, thus helping in vulnerability assessment and enhancing the understanding of potential security weaknesses in web applications. 'pHpmyadmin Shell' operates by leveraging common bypass techniques to gain unauthorized access to the underlying database, making it invaluable for testing the efficacy of security measures against remote execution attacks. Its architecture is crafted to seamlessly integrate with existing server environments, providing testers with a robust platform for comprehensive security evaluations. Ethical hacking communities and professionals use this tool under authorized conditions to ensure that their systems can withstand sophisticated cyber-attacks and to rectify flaws before they can be exploited maliciously. The effective use of PHP web shells like 'pHpmyadmin Shell' underscores the critical need for advanced tools in the continuous battle against cyber threats, making them a cornerstone in the repertoire of tools used for secure server management and backend integrity checks.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.