privdayz v1 shell multi bypass tools
Backdoor ShellPrivdayz v1 Shell excels in advanced penetration testing and security auditing, offering features like bypass capabilities, auto-root for both Linux and Windows, and over 40 integrated tools, including symlink and CGI support.
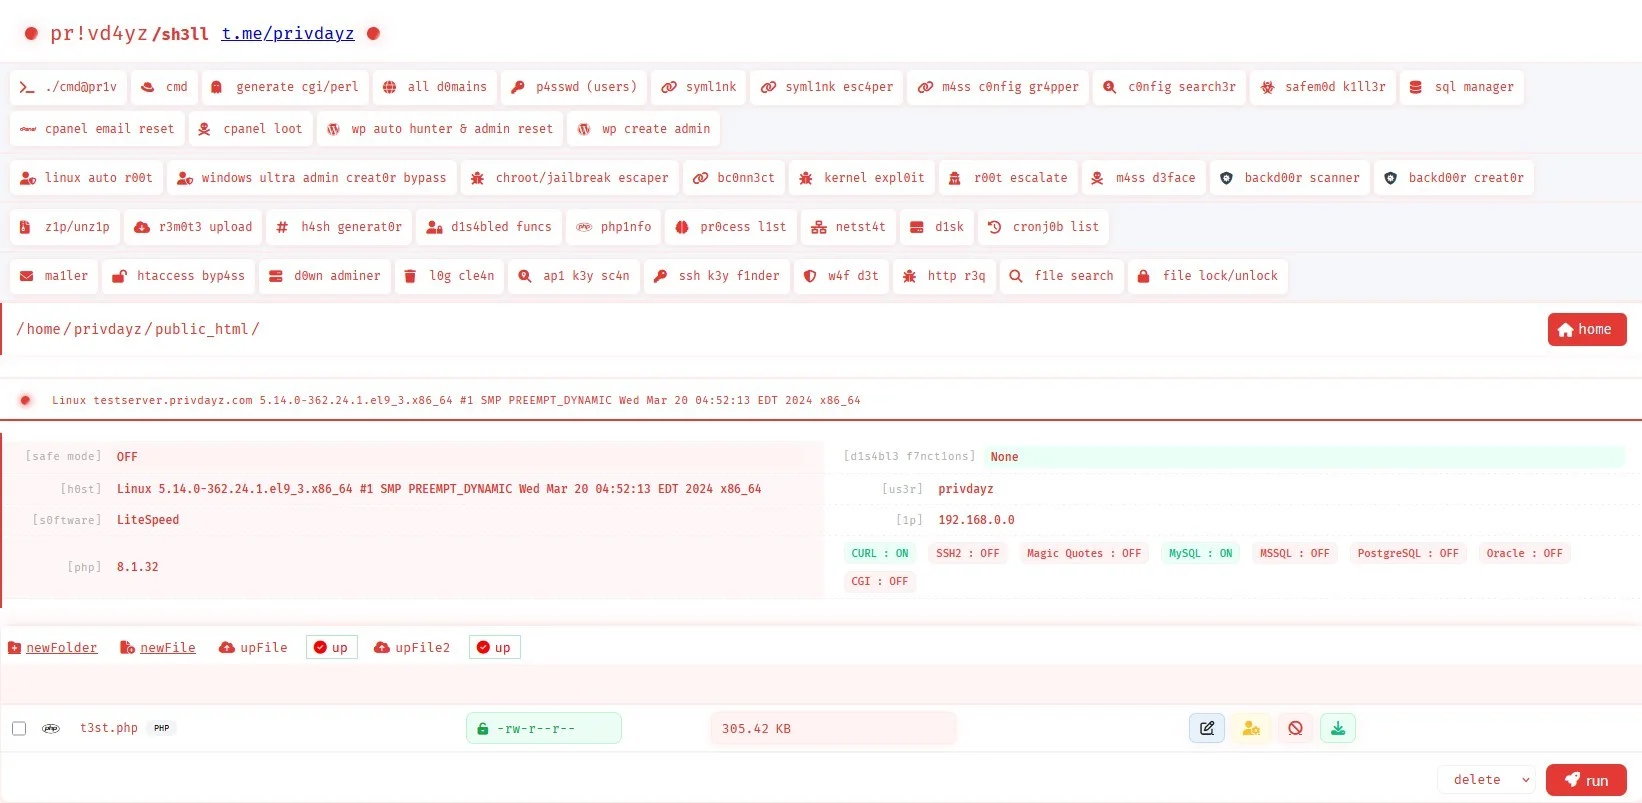
Features
About privdayz v1 shell multi bypass tools
The PHP web shell tool named 'privdayz v1 shell multi bypass tools' is specifically designed for advanced penetration testing, providing a multifaceted approach to backend server management and security auditing through its robust suite of bypass techniques. Crafted with precision for ethical hacking applications, this tool enables security professionals to perform comprehensive vulnerability assessments and simulate sophisticated attack scenarios. Its core functionality revolves around enabling remote execution capabilities, allowing testers to explore and exploit security weaknesses within server environments effectively. The architecture of the 'privdayz v1 shell' is engineered to facilitate seamless navigation through various security layers, enhancing the ability to bypass common and advanced security measures typically encountered during testing phases. This capability makes it an indispensable resource for researchers and cybersecurity practitioners aiming to fortify their infrastructures against potential threats. In essence, 'privdayz v1 shell multi bypass tools' serves as a critical instrument in the toolkit of those committed to maintaining the integrity and security of digital assets while ensuring that all exploration of vulnerabilities is conducted within the bounds of authorized and ethical hacking practices.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.