Gel4y Mini Shell
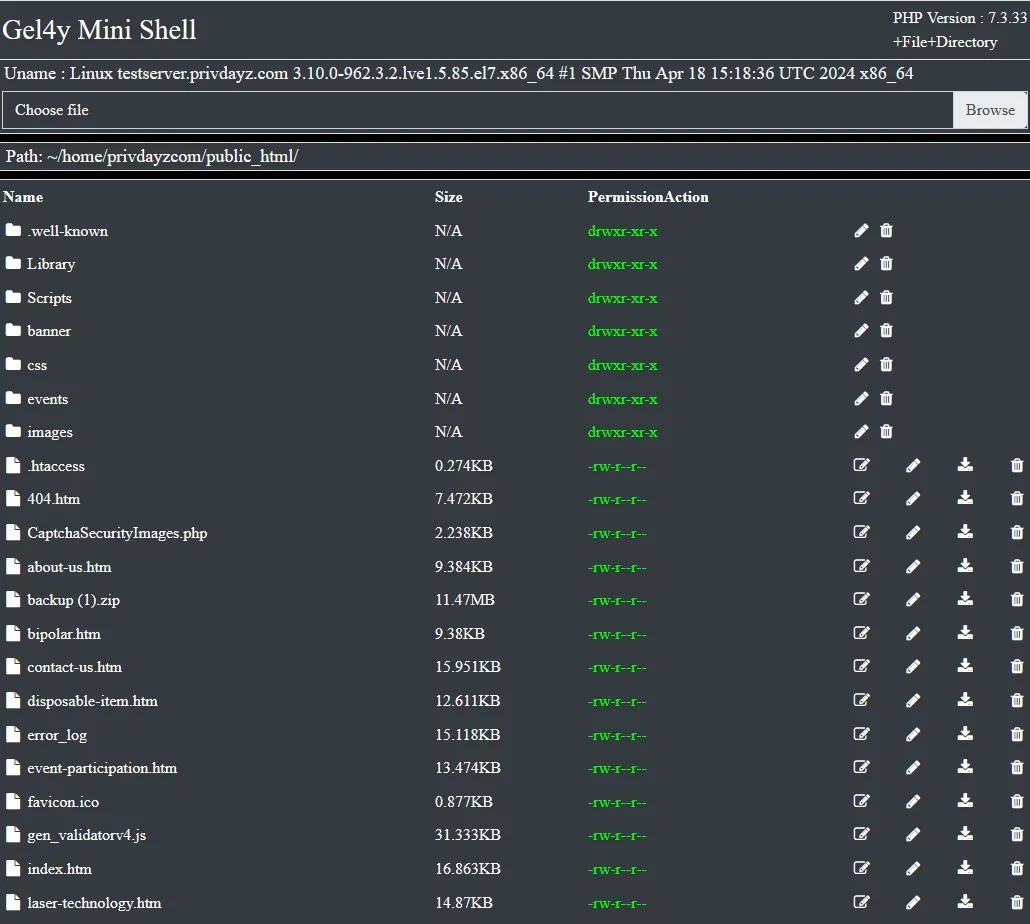
Backdoor ShellGel4y Mini Shell is a PHP-based tool designed for security auditing and penetration testing, enabling users to bypass restrictions and manage server-side operations effectively. Ideal for authorized cybersecurity assessments and enhancing server control.
Features
About Gel4y Mini Shell
The PHP web shell tool named 'Gel4y Mini Shell' serves as a potent resource primarily utilized for backend server management and ethical hacking, particularly in scenarios involving penetration testing and security auditing. This compact yet robust tool facilitates remote execution, enabling cybersecurity professionals to administer commands on a server as if they were operating directly on the system. Its architecture is designed to be lightweight and efficient, ensuring minimal footprint while providing extensive functionality. Gel4y Mini Shell is particularly valued for its ability to bypass standard security protocols, making it a critical asset in vulnerability assessment exercises where testers need to simulate real-world attack scenarios to gauge system robustness. With features tailored for comprehensive backend management, the tool not only allows for executing shell commands but also supports file management, database handling, and running PHP code directly from the browser. This versatility makes it an indispensable utility in the toolbox of professionals engaged in safeguarding digital environments against potential breaches. By leveraging such tools, ethical hackers can identify security weaknesses and help organizations fortify their defenses against malicious attacks. It’s essential, however, to underscore the importance of using such powerful tools strictly within the bounds of legal and ethical guidelines to prevent unauthorized access and ensure the integrity of testing practices.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.