403WebShell Bypass
PHP Shell'403WebShell Bypass' is a PHP web shell tool designed for penetration testing and security auditing, enabling users to bypass server restrictions effectively. Ideal for authorized cybersecurity assessments, it enhances testing precision and access capabilities.
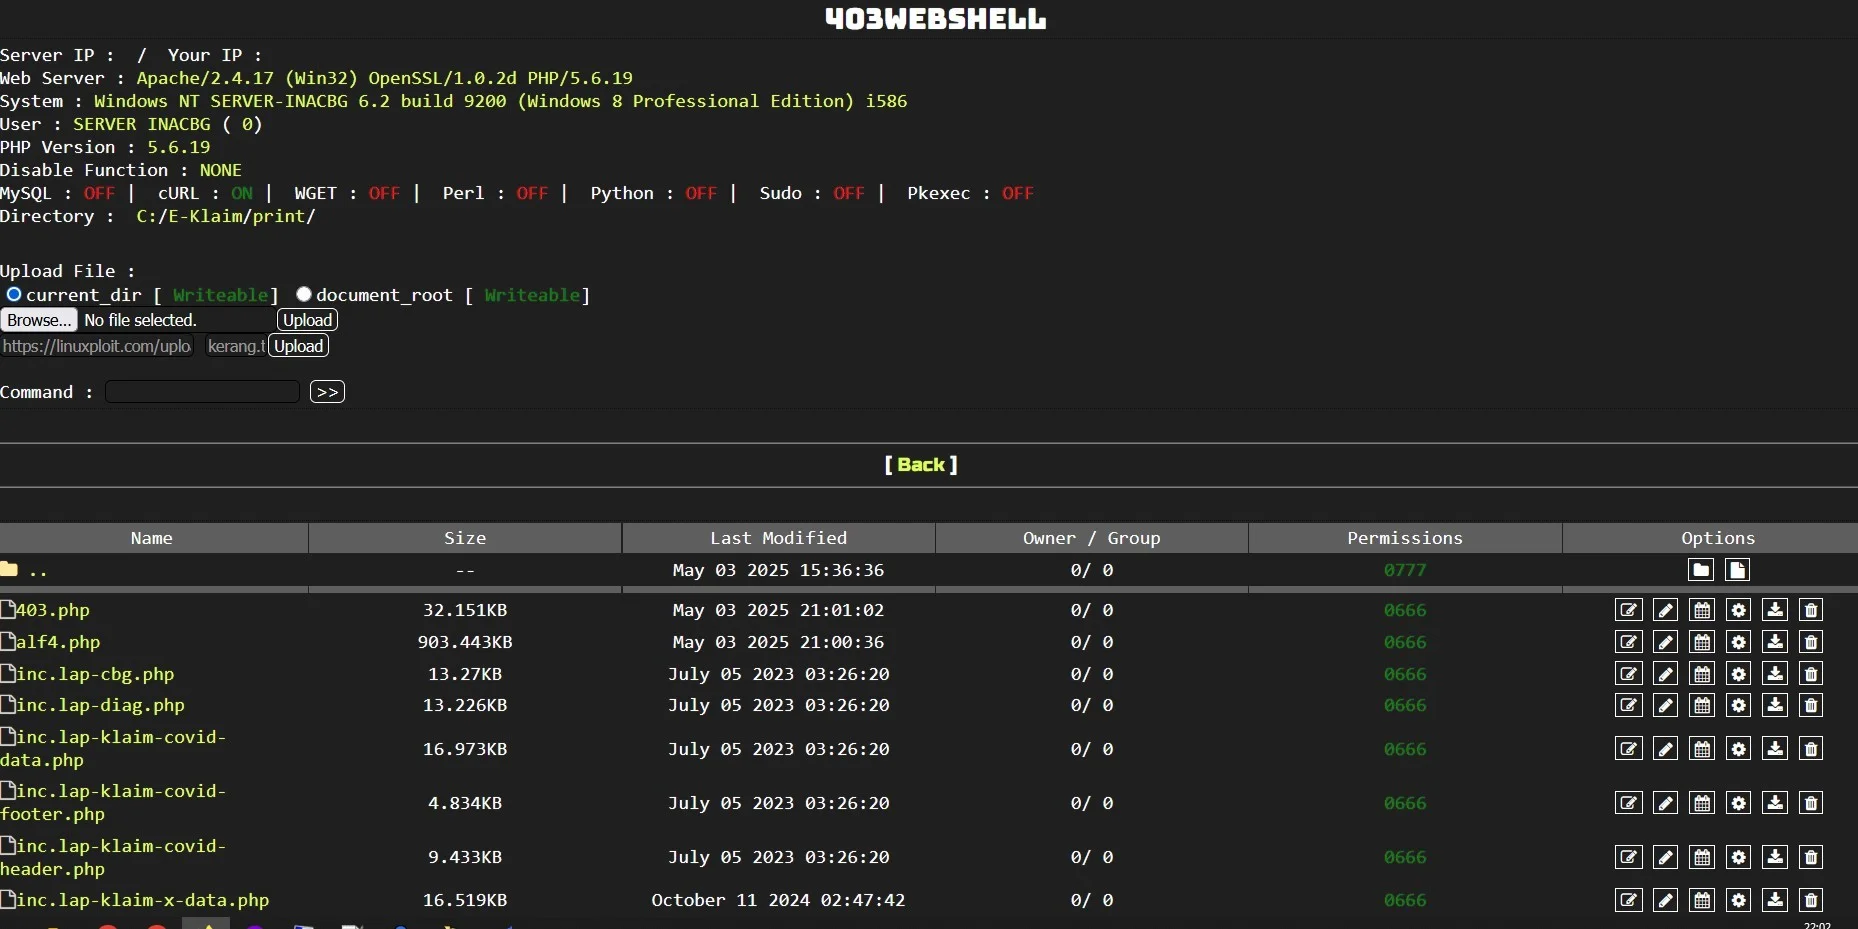
Features
About 403WebShell Bypass
The 403WebShell Bypass is a sophisticated PHP tool engineered for backend server management and penetration testing, specifically tailored to facilitate remote execution and bypass techniques that test the resilience of web servers. This tool is primarily used within the confines of ethical hacking and security auditing to evaluate and strengthen server security by simulating an adversary's attack. Its architecture is meticulously designed to interact seamlessly with server-side scripts, thereby enabling security professionals to probe for vulnerabilities in real-time. Utilizing the 403WebShell Bypass, penetration testers can gain insights into potential security lapses and execute commands that assess the robustness of security protocols. The tool is a pivotal asset in vulnerability assessment, as it allows testers to bypass common security configurations that might otherwise block malicious intrusions. This not only enhances the understanding of possible security weaknesses but also aids in formulating effective countermeasures. It's crucial to note that while the 403WebShell Bypass can be a powerful component in a security toolkit, its use should always be restricted to authorized testing environments to avoid legal and ethical violations. As such, it proves indispensable for IT professionals dedicated to safeguarding digital assets against increasingly sophisticated cyber threats.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.