UCHIHA RAJON Web Shell
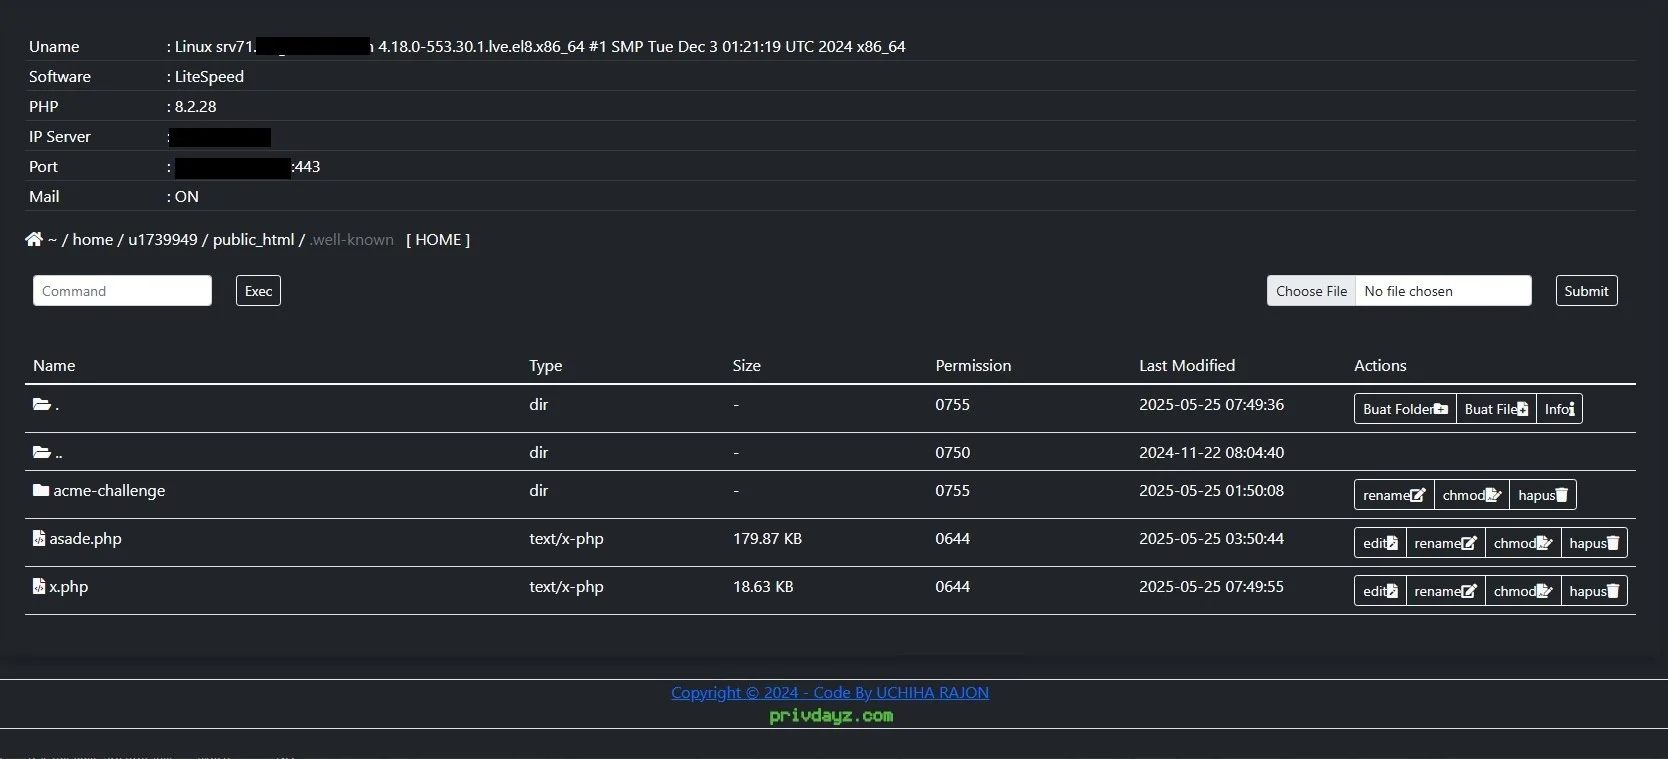
PHP ShellUCHIHA RAJON Web Shell facilitates advanced penetration testing and security auditing, enabling users to bypass standard protocols safely within authorized environments. This tool is essential for assessing and enhancing web application defenses.
Features
About UCHIHA RAJON Web Shell
The UCHIHA RAJON Web Shell emerges as a sophisticated PHP-based tool designed to manage web servers remotely, providing an extensive interface for backend server management, particularly useful in penetration testing and security auditing scenarios. This tool facilitates a streamlined approach to executing commands directly on the server, aiding ethical hackers and cybersecurity professionals in conducting thorough vulnerability assessments and exploring bypass techniques securely. With features tailored for seamless remote execution, UCHIHA RAJON stands out in its ability to interact with server resources, modify files, and execute scripts, all through a web-based interface that requires minimal setup. Importantly, its utility in ethical hacking is underscored by its capacity to simulate various attack scenarios to test the resilience of network systems against unauthorized access. The architecture of UCHIHA RAJON is built to prioritize security, incorporating mechanisms to mask its activities and evade detection, thus serving as a critical tool in the arsenal of developers and IT professionals aiming to fortify their systems. As such, it's imperative that usage of such tools is confined strictly to authorized testing environments to prevent any potential misuse that could compromise data integrity and security.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.