AnonSec Team Backdoor Shell
Bypass Shell'AnonSec Team Backdoor Shell' is a PHP tool designed for security auditing and penetration testing, enabling users to bypass standard access controls to evaluate system vulnerabilities responsibly and effectively.
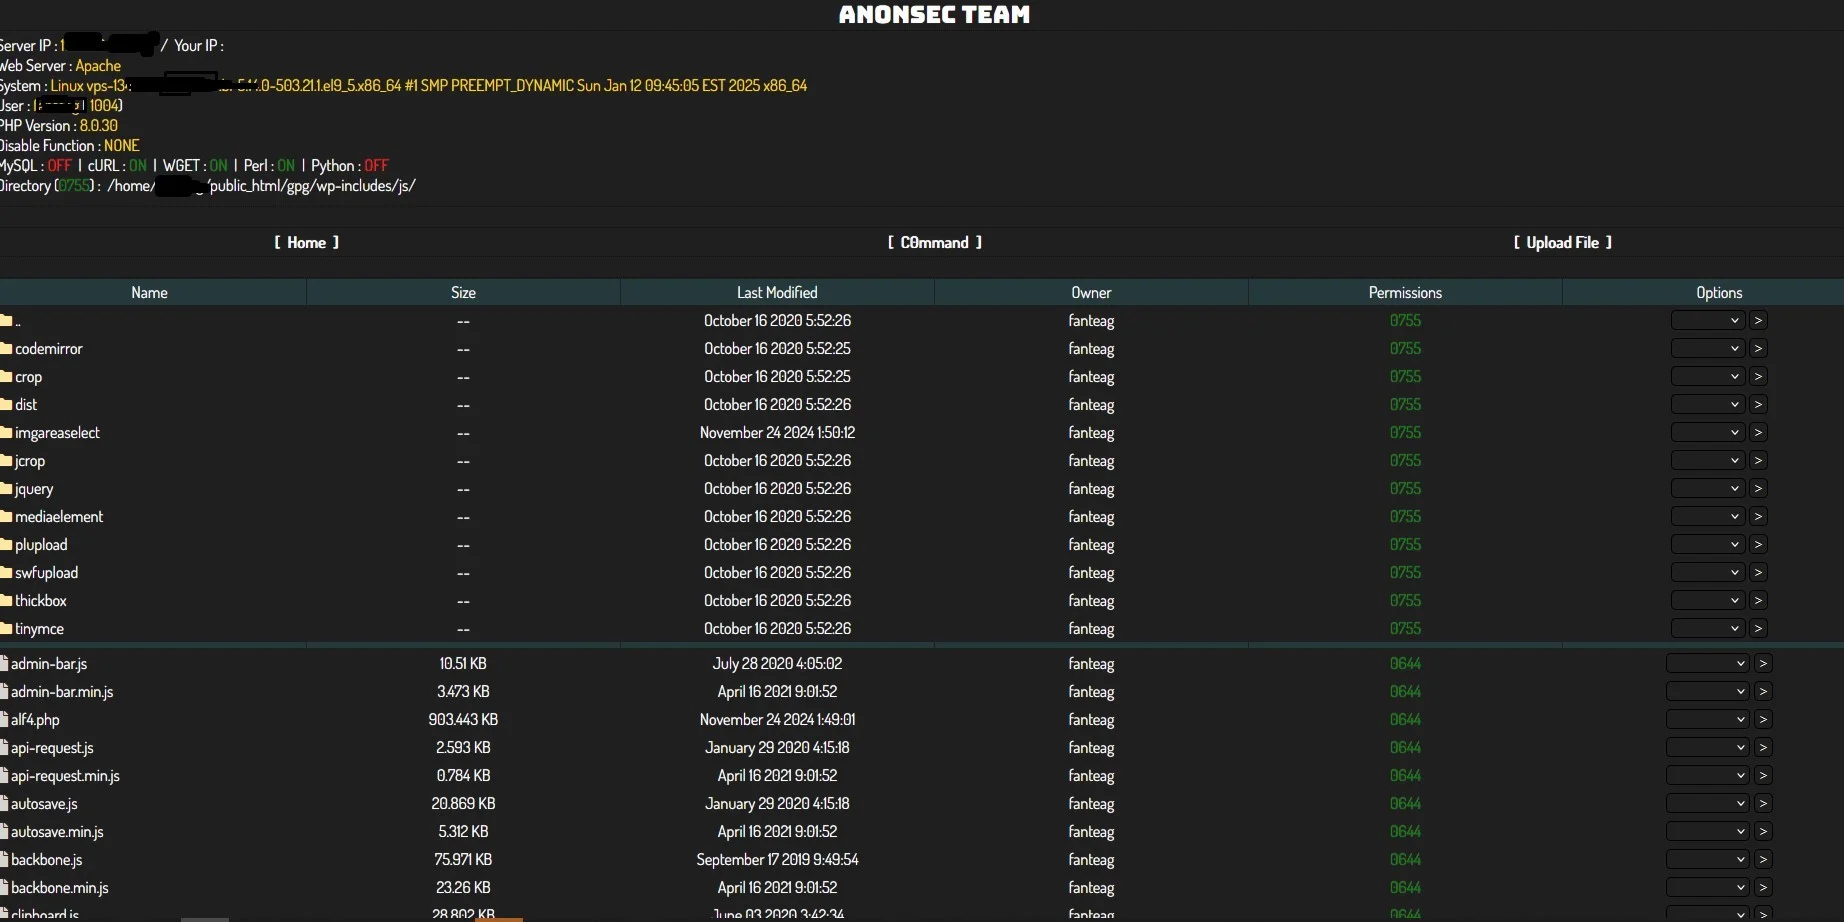
Features
About AnonSec Team Backdoor Shell
The AnonSec Team Backdoor Shell is a PHP web shell tool designed primarily for backend server management, offering cyber professionals a powerful interface for remote execution, penetration testing, and security auditing. Crafted with a focus on bypass techniques, this tool facilitates ethical hacking exercises and vulnerability assessments by enabling direct command execution over web servers. It integrates seamlessly into hidden or neglected features of server environments, allowing testers to simulate advanced cyber-attack scenarios in a controlled manner. With its robust framework, AnonSec Team Backdoor Shell provides an essential utility for cybersecurity experts aiming to understand and fortify the defenses of web applications. Its capabilities are particularly beneficial in identifying potential security flaws that could be exploited maliciously. By offering a comprehensive suite for backend exploration and manipulation, it serves as an invaluable resource in the arsenal of tools used to safeguard digital assets. The tool's architecture is designed to operate under the radar, making it an effective solution for penetration testers and security teams to perform thorough security checks without alerting existing security measures, thereby ensuring that the integrity and security of the system can be tested rigorously and ethically.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.