Back Hack Bypass Shell
Bypass ShellBack Hack Bypass Shell is a PHP web shell designed for advanced penetration testing and security auditing, enabling users to bypass standard access controls efficiently. This tool is crafted for authorized cybersecurity professionals to enhance system defenses.
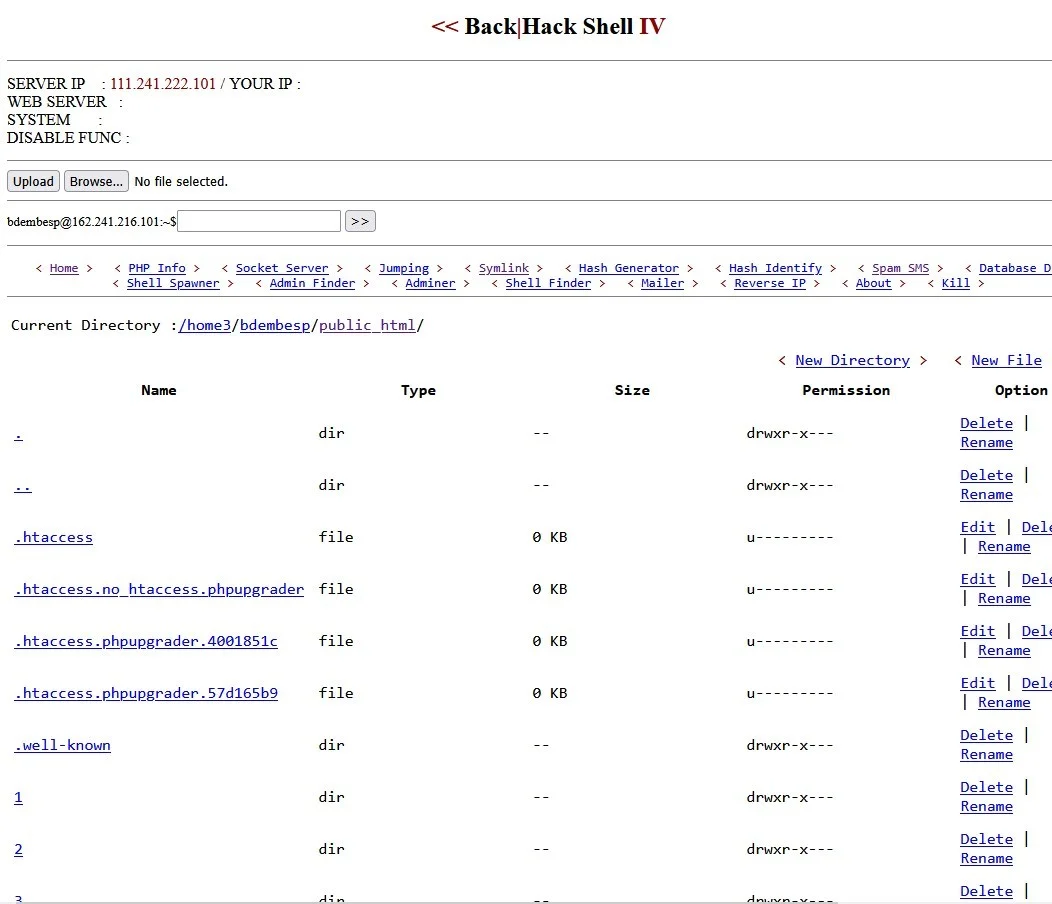
Features
About Back Hack Bypass Shell
The PHP web shell tool, 'Back Hack Bypass Shell', serves as a sophisticated utility designed for backend server management, particularly in scenarios involving security auditing and ethical hacking. Crafted to facilitate remote execution, this tool is integral in penetration testing and vulnerability assessment processes, providing users with the ability to execute commands on a server remotely as part of bypass techniques to assess security measures. Its architecture is streamlined for ease of use yet robust enough to handle complex commands and scripts essential for comprehensive security evaluations. 'Back Hack Bypass Shell' is particularly valued in the cybersecurity community for its effectiveness in demonstrating how attackers can exploit vulnerabilities to gain unauthorized access, thus enabling IT security professionals to better fortify their networks against potential threats. Utilization of this tool is strictly meant for authorized testing and educational purposes to ensure ethical standards are adhered to. By simulating various attack scenarios, it aids in pinpointing weaknesses within the system, thereby enhancing the overall security posture of the infrastructure through meticulous security auditing and ethical hacking practices.
WARNING: This tool is provided for authorized security testing and educational purposes only. Deploying on systems without explicit written authorization violates applicable computer fraud laws (CFAA, CMA, StGB §202a, etc.) and may result in criminal prosecution. The user assumes full responsibility for compliance with all applicable laws.